
Repentigny
IT services in Repentigny: email kept safe from phishing and CEO fraud
Friday, 3:40 p.m. The accounts payable clerk gets two lines from the owner: a supplier has switched banks and must be paid today. The owner wrote nothing. OKTO Solutions helps SMBs block that kind of message, and hold firm when one gets through anyway, from Trois-Rivières, about 109 km from Repentigny.
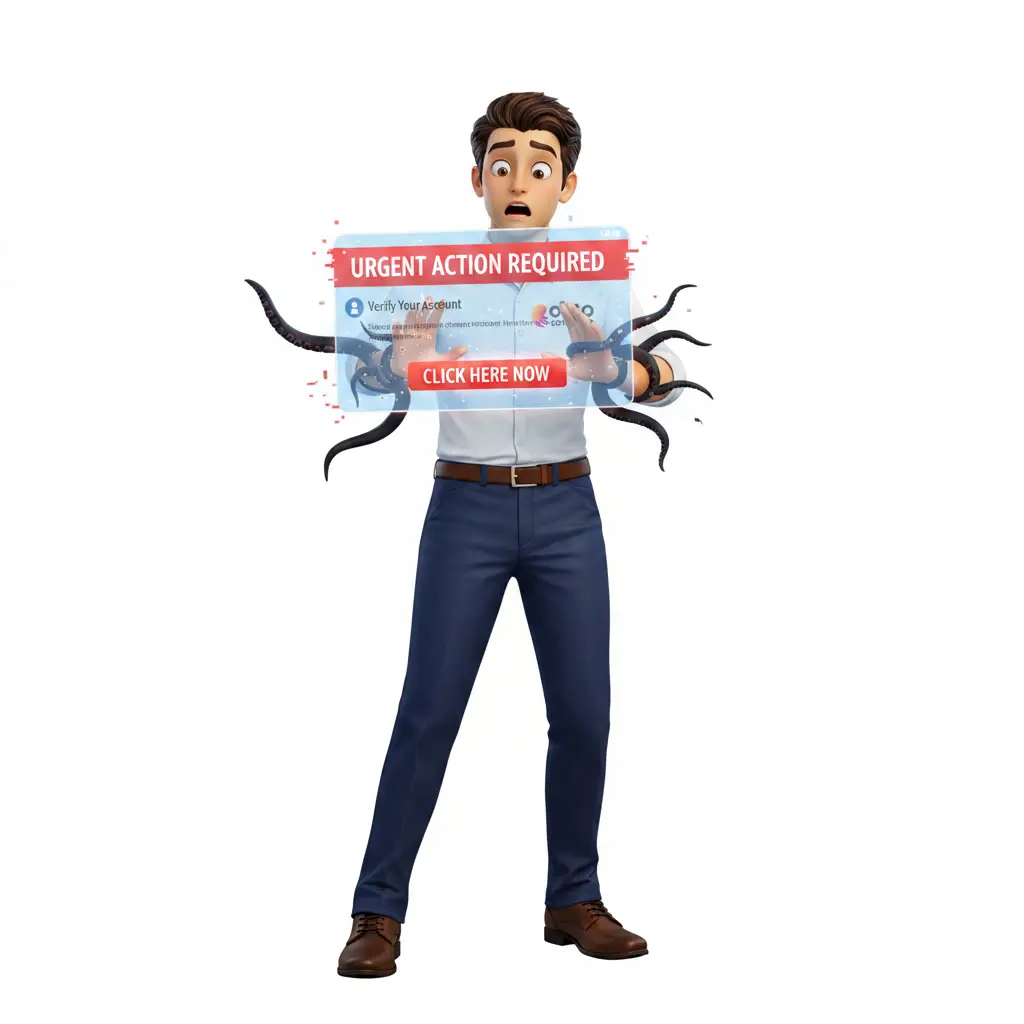
In Repentigny, OKTO Solutions protects an SMB’s email with three measures run together: filtering of incoming messages, domain authentication with SPF, DKIM and DMARC, and an internal rule that has every change of banking details confirmed by phone. The work is done remotely from Trois-Rivières, about 109 km away.
How does a Repentigny SMB protect itself from CEO fraud?
In Repentigny, CEO fraud shows up as an email with no link and no attachment: someone poses as the owner or as a supplier and asks for a wire transfer or a new bank account number. OKTO Solutions offers its services to SMBs in Repentigny from its office in Trois-Rivières, about 109 km away, and handles email protection as one service with three parts. Filtering stops what comes in. Domain authentication with SPF, DKIM and DMARC keeps a stranger from writing in the company’s name: the records are published in a single intervention, then DMARC stays in monitoring mode for 4 to 6 weeks before quarantine and reject. The third part is human. An internal rule has any change of banking details validated by phone, at a number already on file. All of it is set up remotely. OKTO has no office of any kind in Repentigny and announces no travel time for the city.
The scenario
What does email fraud look like in a small business?
Three versions keep coming back. None relies on a software flaw. Each one takes advantage of a work habit.
The boss in a hurry
A brief note signed by the owner, demanding a quiet payment before the day ends. The address looks right, one letter off. Pressure does the rest.
The supplier with a new account
The invoice is genuine in every respect except the bank account number. Nobody notices until the real supplier asks where the money went.
The mailbox already taken
An employee typed a password into a fake Microsoft 365 page. The attacker now replies from inside a real conversation thread. By eye, it is close to impossible to spot.
Antivirus software does nothing for these three cases. The answer lies in filtering, domain identity and people’s reflexes, as our page on email protection for SMBs explains.
Under the magnifying glass
How do you recognize a phishing message?
Seldom at first glance. The logo is right and so is the tone. The clues sit elsewhere, where nobody looks on a busy Tuesday morning.
The sender’s address comes first: a lookalike domain swaps an “m” for “rn” and slips by. Then the link, which does not open the page the button promises. Last, the technical header, which shows whether the sender was allowed to write for that domain. Filtering reads all of this before the email reaches the mailbox, so most forged messages never land in front of an employee.
For the ones that make it through, two aids remain. A banner marks every email coming from outside, which gives the fake boss away. And OKTO’s vCIO module includes four phishing simulations a year, with follow-up on who clicked.
 OKTO mail filter
A fake password notice taken apart: the real link, the lookalike domain, then the quarantine.
If it already happened
What should you do once an employee has entered a password?
Five actions, in this order. The first cannot wait until tomorrow.
- Change the password and revoke sessions. While a session stays open, the new password locks nobody out.
- Check the mailbox rules. Creating a rule that hides or forwards replies is an intruder’s first move. Any rule that is not legitimate gets deleted.
- Read the sign-in history. It shows where the intruder came in from and what may have been viewed.
- Warn the contacts. Customers and suppliers who were exchanging with that person need to know a message in that name may be false.
- Document the incident. Law 25 requires a register of confidentiality incidents, and a notice to the Commission d’accès à l’information if the risk of injury is serious.
Your domain name
How do you stop a stranger from writing in your name?
Left unprotected, your address can be displayed by anyone on an email they send. Your customers cannot tell the difference. Three public records attached to your domain close that door.
SPF names the servers allowed to send mail for you. DKIM signs every outgoing message. DMARC tells receiving servers what to do with a message lacking the right signature: let it through, quarantine it or reject it. It is the only measure that protects people outside your company.
Nothing is tightened before it has been observed. A policy set too quickly cuts off the newsletter, appointment reminders and automatic invoices. During the monitoring period, every service already sending in your name is identified, from the accounting software to the website form. To find out where your settings really stand, there is the cybersecurity audit for SMBs.
SPF, DKIM and DMARC turn green, then the unknown sender is rejected once the policy tightens.
The ground
Repentigny, about 109 km from our office
Repentigny belongs to the L’Assomption regional county municipality, in Lanaudière. Autoroute 40 is the main highway serving the city.
For this service, distance weighs little. A DNS record, a Microsoft 365 policy or a mailbox rule can be read and corrected remotely, and that is how the service is offered in Repentigny. We have neither premises nor a technician on site there. Trips start from Trois-Rivières and are booked by appointment, when the mandate requires it.
Email protection is part of our managed IT services, offered as Base, Standard and Complet plans. The legal side, meaning the incident register and the notice to the people affected, is explained on the Law 25 compliance page. Every territory is listed on the service areas page, and the contact page is the place to ask for a review of your current configuration.
Questions and answers
Your questions about email protection in Repentigny
What exactly is CEO fraud?
Does Microsoft 365 not protect our email already?
How long before DMARC rejects forged messages?
Can filtering hold back real email?
Do you have to come to Repentigny to set up the protection?
Does a hacked mailbox fall under Law 25?
Is your email in Repentigny protected?
We read the configuration of your domain and your mailboxes, then tell you what is missing. If everything is in place, we say that too.
Reviewed by Antonio Pazzi, president of OKTO Solutions · updated